What problems does Gotel solve?
Reliance on alerts
Automated alerts do not catch every threat or its context.
Unidentified threats
Difficulty identifying threats with no known signature.
Channels off the radar
Lack of visibility into communications on underground channels.
Scattered sources
Information spread across sources and tools makes investigation harder.
Lack of context
No context on who is behind a threat.
Late ransomware detection
Inability to anticipate ransomware attacks before impact.
Key capabilities of Gotel
In-depth investigation
Widen the context around a threat by connecting indicators, infrastructure, credentials, campaigns and other related signals.
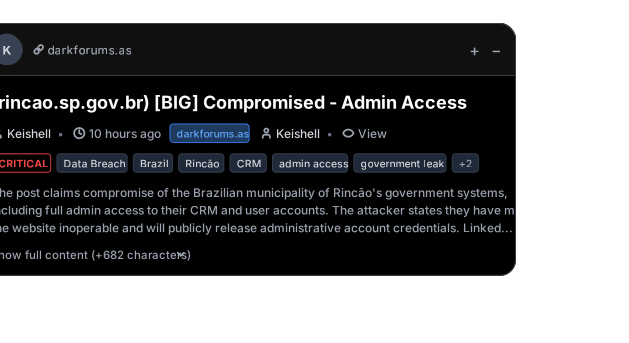
Underground forum analysis
Follow discussions, access trading and other relevant activity in environments used by cybercriminals.
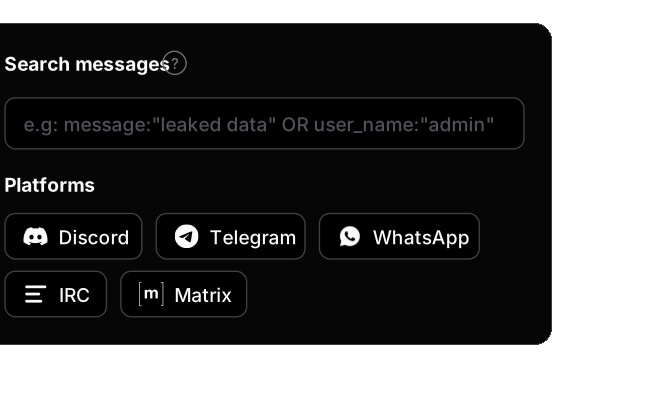
Channel and group monitoring
Monitor closed channels and communities used by threat actors to spot relevant signals related to your organization or your sector.
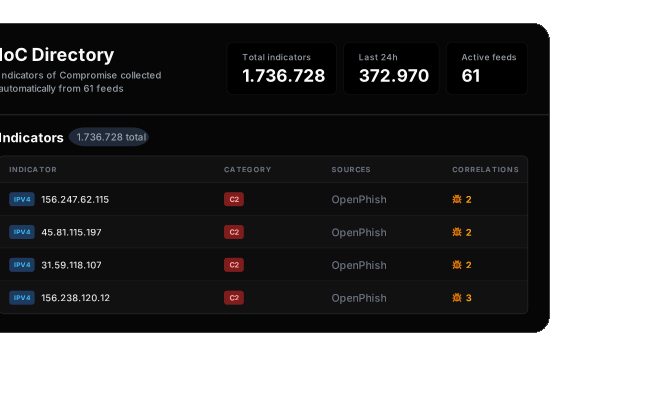
Indicator correlation
Relate IPs, domains, URLs, hashes and other IoCs to identify connections between infrastructure, campaigns and malicious activity.
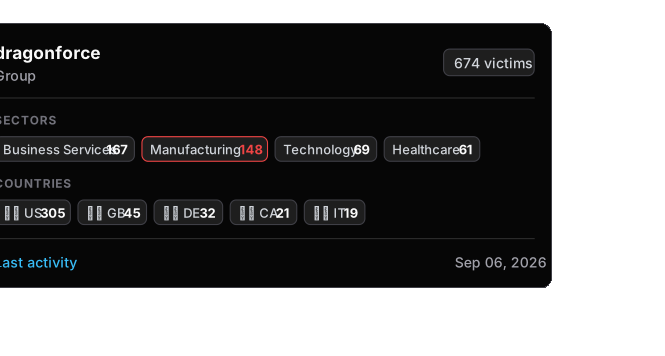
Threat actor context
Track groups, infrastructure, patterns of operation and activity history to deepen understanding of a threat.
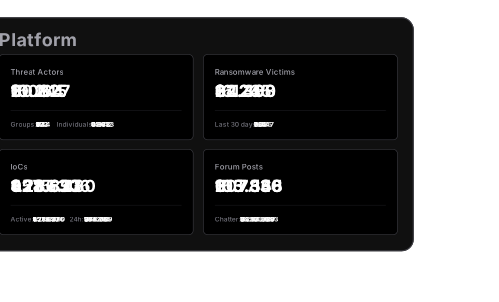
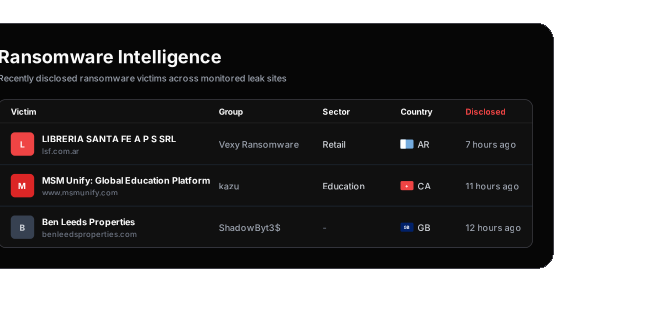
Ransomware Intelligence
Track ransomware groups, campaigns, victims, malware and TTPs to spot relevant activity and trends.
Understand what lies
behind every threat.
Get more context on indicators, infrastructure, campaigns and relevant activity to support security decisions.